Whitepaper
RBI: The Misreading Tax
Many Indian financial institutions still assume RBI requires on-premises deployment. It does not. This whitepaper explains what RBI actually requires, why the misreading persists, and how that assumption can increase cost, delay security decisions, and slow data visibility.
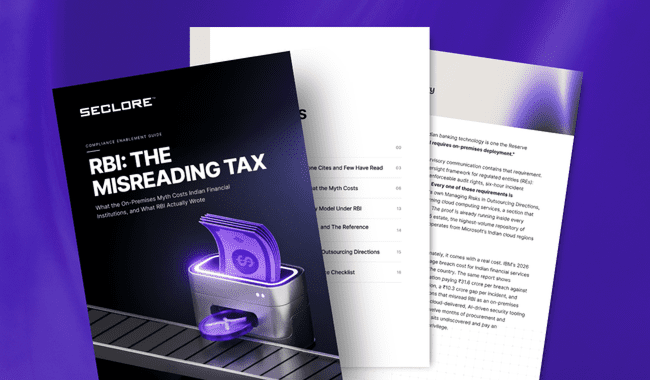
What to Expect

Separate regulatory text from institutional assumptions, with a clear view of residency, audit, incident reporting, governance, and cloud oversight.

See how on-premises assumptions can add infrastructure spend, delay deployment, and extend the period sensitive data remains undiscovered.

Review how cloud deployment can map to RBI requirements through shared responsibility, reference architecture, clause mapping, and due diligence.
Inside the Whitepaper
A practical guide to what RBI guideline on deployment requires, what it does not, and how regulated entities can assess cloud-based security architecture with confidence.
Where the Myth Comes From
Trace how internal risk policies and procurement language turned an interpretation of RBI guidance into an assumed deployment requirement.
The AI Infrastructure Problem
See why fixed infrastructure can create GPU, capacity, cost, and deployment challenges for modern AI-powered data security programs.
Who Owns What
Understand the responsibilities of regulated entities, cloud providers, and security vendors under RBI guidelines.
Cloud Architecture Under RBI
See how an India-based cloud deployment can address residency, access control, encryption, and recovery requirements.
Clause by Clause Mapping
Map key provisions of the 2025 Outsourcing Directions to controls, responsibilities, and supporting evidence.
Due Diligence Checklist
Use eight practical questions to assess data location, incident response, subcontractors, audit rights, and exit planning.
Who should read this?
This whitepaper is for technology, security, risk, and compliance leaders at RBI-regulated entities assessing cloud deployment, data residency, and outsourcing requirements.
1
CISOs and Security Leaders
Responsible for data protection strategy, security architecture, breach readiness, and proving that controls meet regulators’ expectations.
2
CIOs and IT Leaders
Making deployment and infrastructure decisions that balance regulatory requirements, cost, operational needs, and access to modern security capabilities.
3
Risk and Compliance Leaders
Interpreting regulatory requirements, reviewing outsourcing arrangements, and maintaining evidence for audits, supervision, incident reporting, and governance reviews.
4
Cloud and Enterprise Architects
Assessing whether cloud architecture can meet regulatory requirements for residency, access control, business continuity, auditability, and oversight.
5
Third Party Risk and Procurement Teams
Evaluating service providers, contractual safeguards, subcontractors, exit plans, incident obligations, and the evidence required during due diligence.
Related Resources
TRUSTED BY INDUSTRY-LEADING ENTERPRISES